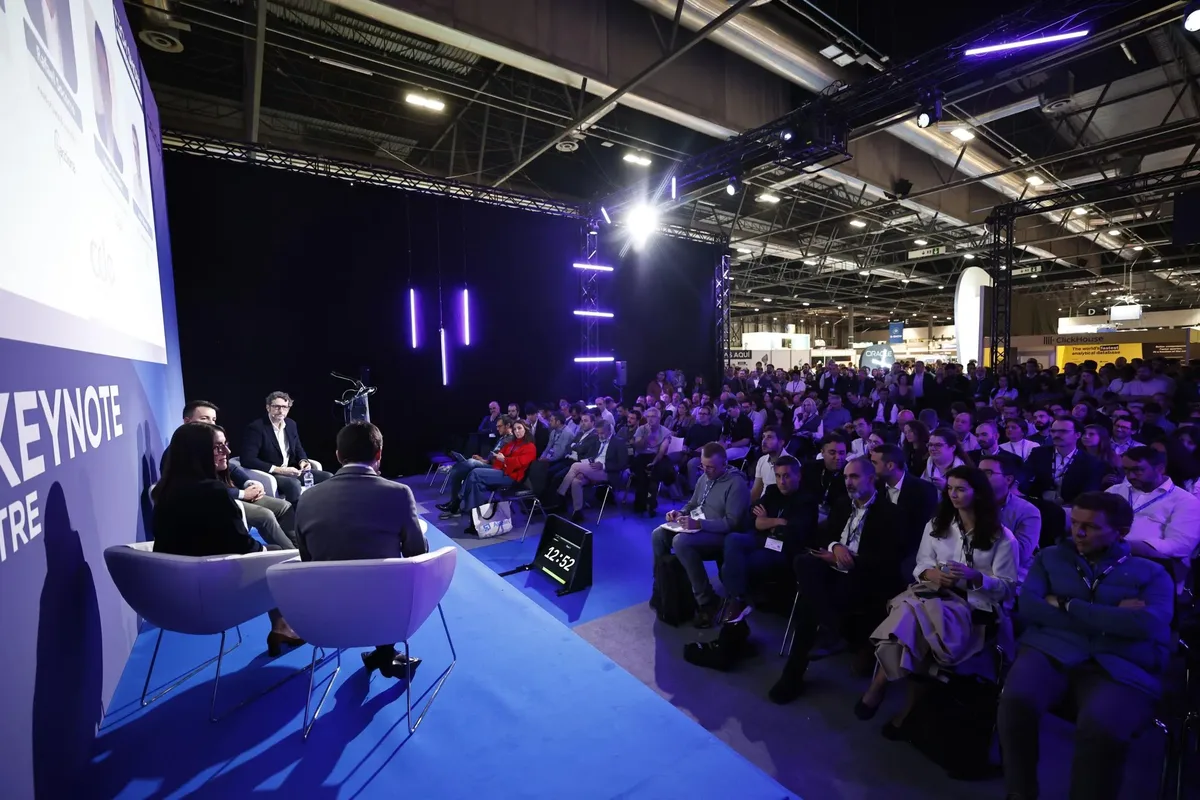
Model proliferation and embedded AI components are reshaping the attack surface for security teams. Against that backdrop the AI Sec Summit 2026 takes place on 7 May 2026 in London, a focused one-day forum on AI risk and cybersecurity for security leaders and technical teams.
Dates and venue for AI Sec Summit 2026
The summit runs on 7 May 2026 at Park Plaza Victoria, London. Venue details in event materials list 239 Vauxhall Bridge Road, London, SW1V 1EQ. The format is structured around technical sessions and real-life case studies.
Technical tracks on the program
Program topics outlined for the summit address operational challenges of enterprise AI. Key areas include preventing accidental data exfiltration into LLMs, hardening MLOps pipelines, supply-chain risks in model weights and datasets, AI-driven offensive techniques, control boundaries for human-AI interaction, resilience engineering and the regulatory landscape impacting AI controls.
Key figures and operational risk indicators
Pre-event briefing materials include several metrics underlining the issue. Incidents related to users sending sensitive data to generative AI reportedly doubled year on year, with an average organisation recording 223 GenAI-related data-policy violations per month. IBM’s 2025 breach research found one in five studied organisations experienced a breach linked to shadow AI, and organisations with high levels of unapproved AI usage faced up to $670,000 in additional breach costs. The materials also cite that 97% of organisations reporting AI-related incidents lacked appropriate AI access controls. Other cited trends show a 97% rise in risky prompts during 2025 and a notable increase in prompt-injection detections in 2026.
How to approach B2B prospecting at AI Sec Summit 2026
Prospecting should target concrete control gaps. Lead with capabilities for discovery of embedded models, prompt logging and identity-bound access controls. Demonstrate integration with existing IAM and audit systems and provide short technical proofs of concept that show how your solution handles prompt injection scenarios and autonomous agent containment.
During meetings focus on persona-driven outcomes. CISOs and security architects value evidence of end-to-end visibility and governance over broad feature lists. Technical artefacts such as audit logs, sample retention policies and MLOps hardening checklists open more substantive procurement conversations than marketing decks.
Pre-event checklist for technical teams
Prepare documentation on model supply-chain assessments, data classification for LLM inputs and resilience tests for autonomous features. The program lists regulatory touchpoints including the EU AI Act, NIS2, DORA and GDPR; mapping product controls to those frameworks will sharpen vendor conversations.
Final note: treating AI as both a data-egress channel and an attack surface is now operationally necessary. Vendors and teams that can show measurable controls for discovery, access and fail-safe operation will find clearer procurement paths. Registration and practical details are available at the event website http://akjassociates.com/event/aisec